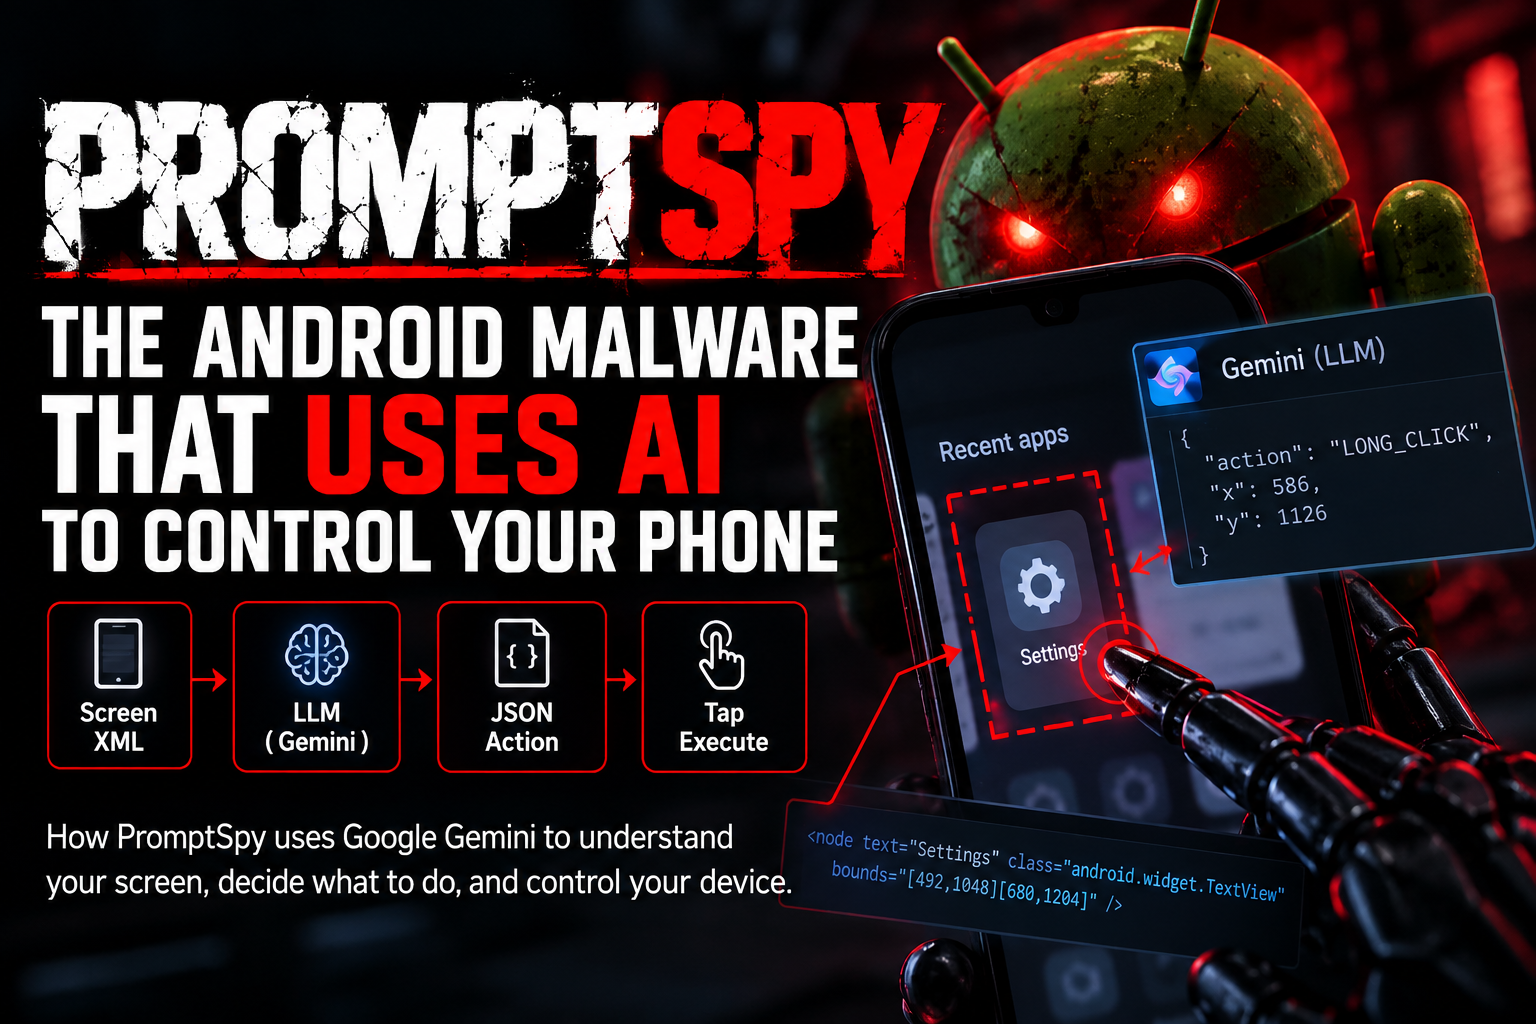
The AI Inside the Malware
For years, one of the biggest discussions around AI and cybersecurity was whether attackers would use AI to write malware faster.
Now there is a more interesting problem:
What happens when attackers put AI directly inside the malware's execution loop?
ESET researchers uncovered PromptSpy, an Android spyware sample that embeds a live generative AI model—Google Gemini—into its runtime execution flow.
PromptSpy doesn't use AI simply to generate malware code.
Instead, it uses AI as a real-time decision-maker.
The malware can analyze the victim's screen, understand the current interface, decide what action should be performed, and then execute that action.
This approach solves a long-standing problem for Android malware: different devices don't have identical interfaces.
Why Traditional Android Malware Can Break
Android devices have different manufacturers, screen sizes, languages, and customized interfaces.
A traditional malware developer might create a hardcoded automation sequence such as:
Tap a specific coordinate.
Find a button with a specific name.
Perform a long press.
Continue to the next step.
That works until the interface changes.
A button might appear in a different location on Samsung One UI compared with Xiaomi HyperOS or a Google Pixel.
Even a small UI change can cause a hardcoded automation sequence to fail.
PromptSpy takes a different approach.
Instead of relying entirely on fixed coordinates, it uses an LLM to interpret the current interface and decide what to do next.
How PromptSpy Uses AI to Control the Device
PromptSpy is primarily a VNC-based spyware tool. According to the analysis in the source, it can intercept lockscreen PINs, record pattern-unlock activity, monitor the screen, and provide attackers with remote control. Pasted text
One of the interesting parts of its implementation is how it attempts to keep itself active in Android's Recent Apps interface.
The process works as a feedback loop:
1. Capture the Current Screen
Using Android's Accessibility Service, PromptSpy extracts the current UI hierarchy into XML.
The XML contains information about visible elements, including text, element types, and their screen boundaries.
2. Send the UI to the LLM
The malware sends that UI information to Gemini together with a system prompt explaining the goal.
The model is effectively being asked:
“Look at the current interface and determine what action I should perform next.”
3. Receive a Structured Action
The LLM responds with structured instructions describing the action.
For example, the response can specify a long click and the coordinates where it should happen.
4. Execute and Verify
PromptSpy performs the action.
It then captures the updated interface and sends the new state back to the model.
The model determines whether the previous action succeeded or whether another action is required.
This creates an autonomous loop:
Observe → Analyze → Act → Observe Again
That is what makes this approach particularly interesting.
The Malware's Actual AI Prompt
The most interesting part of the analysis is that the malware doesn't simply ask the model a generic question.
It provides a structured instruction set.
The prompt tells the AI to analyze Android UI XML, understand element boundaries, calculate coordinates, and return operation instructions in JSON format. It also tells the model not to assume that an operation succeeded without seeing evidence of success.
This is important because it turns the LLM into something closer to an agentic control component rather than a simple text-generation tool.
The malware can provide the current state.
The AI decides what should happen next.
The malware executes the decision.
Then the process repeats.
What the AI Response Looks Like
The analysis provides an example where the model identifies an application inside the Recent Apps screen and decides that the next action should be a long click.
The response includes the action type and coordinates, such as:
Action:
LONG_CLICKX coordinate:
586Y coordinate:
1126
The malware can then translate that response into an actual interaction with the device. Pasted text
This is the important shift.
The malware isn't blindly executing a predefined sequence.
It is using an AI model to interpret the current state before deciding what to do.
PromptSpy Also Tries to Prevent Removal
The malware doesn't stop after maintaining its presence in Recent Apps.
According to the analysis, when a victim attempts to remove it through Android's application settings, PromptSpy places transparent overlays over options such as Uninstall and Force Stop.
The victim can interact with the screen, but those controls are effectively blocked.
The source notes that rebooting into Android Safe Mode may then be required to remove the malware.
This demonstrates another important capability:
The malware isn't only controlling the device—it is actively interfering with the victim's attempts to regain control.
Why This Changes the Malware Problem
PromptSpy is interesting not simply because it uses an LLM.
The bigger idea is adaptive malware behavior.
Traditional UI automation depends heavily on assumptions:
The button is in this location.
The interface looks like this.
The text is in this language.
The menu has this structure.
An LLM can work with the meaning and structure of the interface instead.
That potentially makes malware more adaptable across different devices, screen layouts, languages, and Android interfaces. Pasted text
The Weakness in PromptSpy's Approach
There is also an important limitation.
The analysis notes that PromptSpy contains a hardcoded Gemini API key.
That creates a potential point of failure because the key can potentially be identified and revoked by the relevant provider.
But the bigger concern is what happens if future malware uses on-device small language models instead.
If the model runs locally, malware may not need to communicate with an external AI API for every decision.
That could make this type of architecture considerably harder to disrupt through API-key revocation.
What Defenders Should Look For
Traditional signature-based detection may not be enough for malware that dynamically changes how it interacts with a device.
The source highlights a particularly interesting behavioral pattern:
Untrusted application + Accessibility permissions + UI XML extraction + frequent HTTPS communication with an external AI service.
That combination is much more interesting from a detection perspective than looking for a single malicious file signature.
Defenders should pay particular attention to:
Unexpected Accessibility Service usage
Applications requesting powerful accessibility permissions without a legitimate reason
Rapid UI hierarchy collection
Suspicious remote-control behavior
Repeated outbound communication with AI infrastructure
Applications attempting to interfere with uninstall or force-stop actions
The goal is to detect behavior, not just known malware hashes.
The Bigger Picture
PromptSpy demonstrates a different direction for AI-assisted malware.
The concern isn't only:
“Can AI help attackers write malware?”
It's also:
“Can malware use AI to make decisions while it is running?”
That distinction matters.
A traditional malware sample follows instructions written by its developer.
An AI-assisted malware architecture can potentially observe an environment, interpret what it sees, select an action, execute it, and evaluate the result.
That's much closer to an agentic system.
PromptSpy currently uses this approach for a relatively specific purpose, but the underlying architecture could potentially be applied to much broader automation tasks.
Final Takeaway
PromptSpy is an important example of how the relationship between AI and malware is changing.
The interesting part isn't that malware can call an AI API.
It's that the AI becomes part of the malware's decision-making loop.
Observe → Analyze → Act → Verify → Repeat
That allows malware to move away from rigid, hardcoded automation toward behavior that can adapt to the environment it encounters.
Today, PromptSpy demonstrates this concept through Android UI automation.
Tomorrow, similar architectures could potentially make other forms of malware more adaptive.
For defenders, that means detection needs to evolve from:
“Do we recognize this malware?”
to:
“Does this application behave like something that shouldn't be happening?”
No comments yet.